
ISO 27001 · Israel's privacy regulations · client requirements
Meet information security requirementsand reduce your business risk
We help businesses and organizations:
- Comply with Israel's Privacy Protection Law
- Get ready for ISO 27001 certification
- Meet their clients' information security requirements
Through a smart platform and hands-on expert guidance, with no need to build an in-house security team.
 Personal guidance
 In the pressThe system translates the answers through smart logic and produces, in a short time, a risk register, procedures and tailored policy documents.
Clients & partners
You have reached the point where privacy requirements need handling
Meanwhile, putting it off can cost you. You are exposed to:
- Fines
- Gaps left unaddressed
- Large clients' requirements that catch you unprepared
Between managing staff, clients and day-to-day work, it is hard to make time for a process that looks complex and expensive. Yet the business has reached the stage where it is no longer optional, whether you have more than 5 employees or a deal with a large client whose security requirements oblige you to meet the standards.
At GRCistant we help you map, organize and meet every privacy and information security standard, ISO 27001 included, with personal guidance built on experience guiding dozens of organizations to compliance, easily and quickly, through a smart platform and hands-on expert guidance.
In a short scoping call:
- 01We map the gaps together
- 02We define what needs doing
- 03We build you a focused work plan
Why work with us?
- A tailored processA work plan built around the gaps we mapped together in the scoping call.
- A dedicated expert at your sideOmri Saar, CISO and information security consultant, guides you all the way.
- Fast30 days on average to a full mapping for ISO 27001 readiness
Let's book an intro call
Leave your details and we will get back to you within one business day.
- Reply within one business day
- Free first scoping call
- A quote with clear pricing and timeline
Nice to meet you,
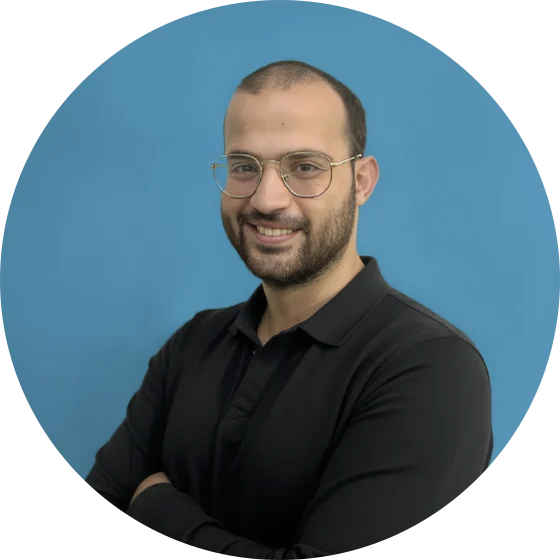
I'm Omri Saar
Founder & CEO, GRCistantI've spent close to a decade in cybersecurity and information security. Today I'm an information security manager (CISO) and a security and compliance consultant, and across my roles I've guided dozens of organizations to ISO 27001 and SOC 2 certification and to compliance with Israel's Privacy Protection Regulations.
GRCistant started at 2 a.m. in the field, during one of my reserve duty call-ups, staring at yet another certification spreadsheet. I asked myself what the client really needed, and what I was doing only because that's how it had always been done. The answer is a platform that shows clients where they stand and streamlines the manual work, with human guidance wherever judgment is needed. Security is an ongoing process, not a list of administrative tasks.
- Hands-on CISO experience
- Led an organization's information security
- CISO training
- Technion, Israel Institute of Technology
- M.A., magna cum laude
- Bar-Ilan University, cybersecurity specialization
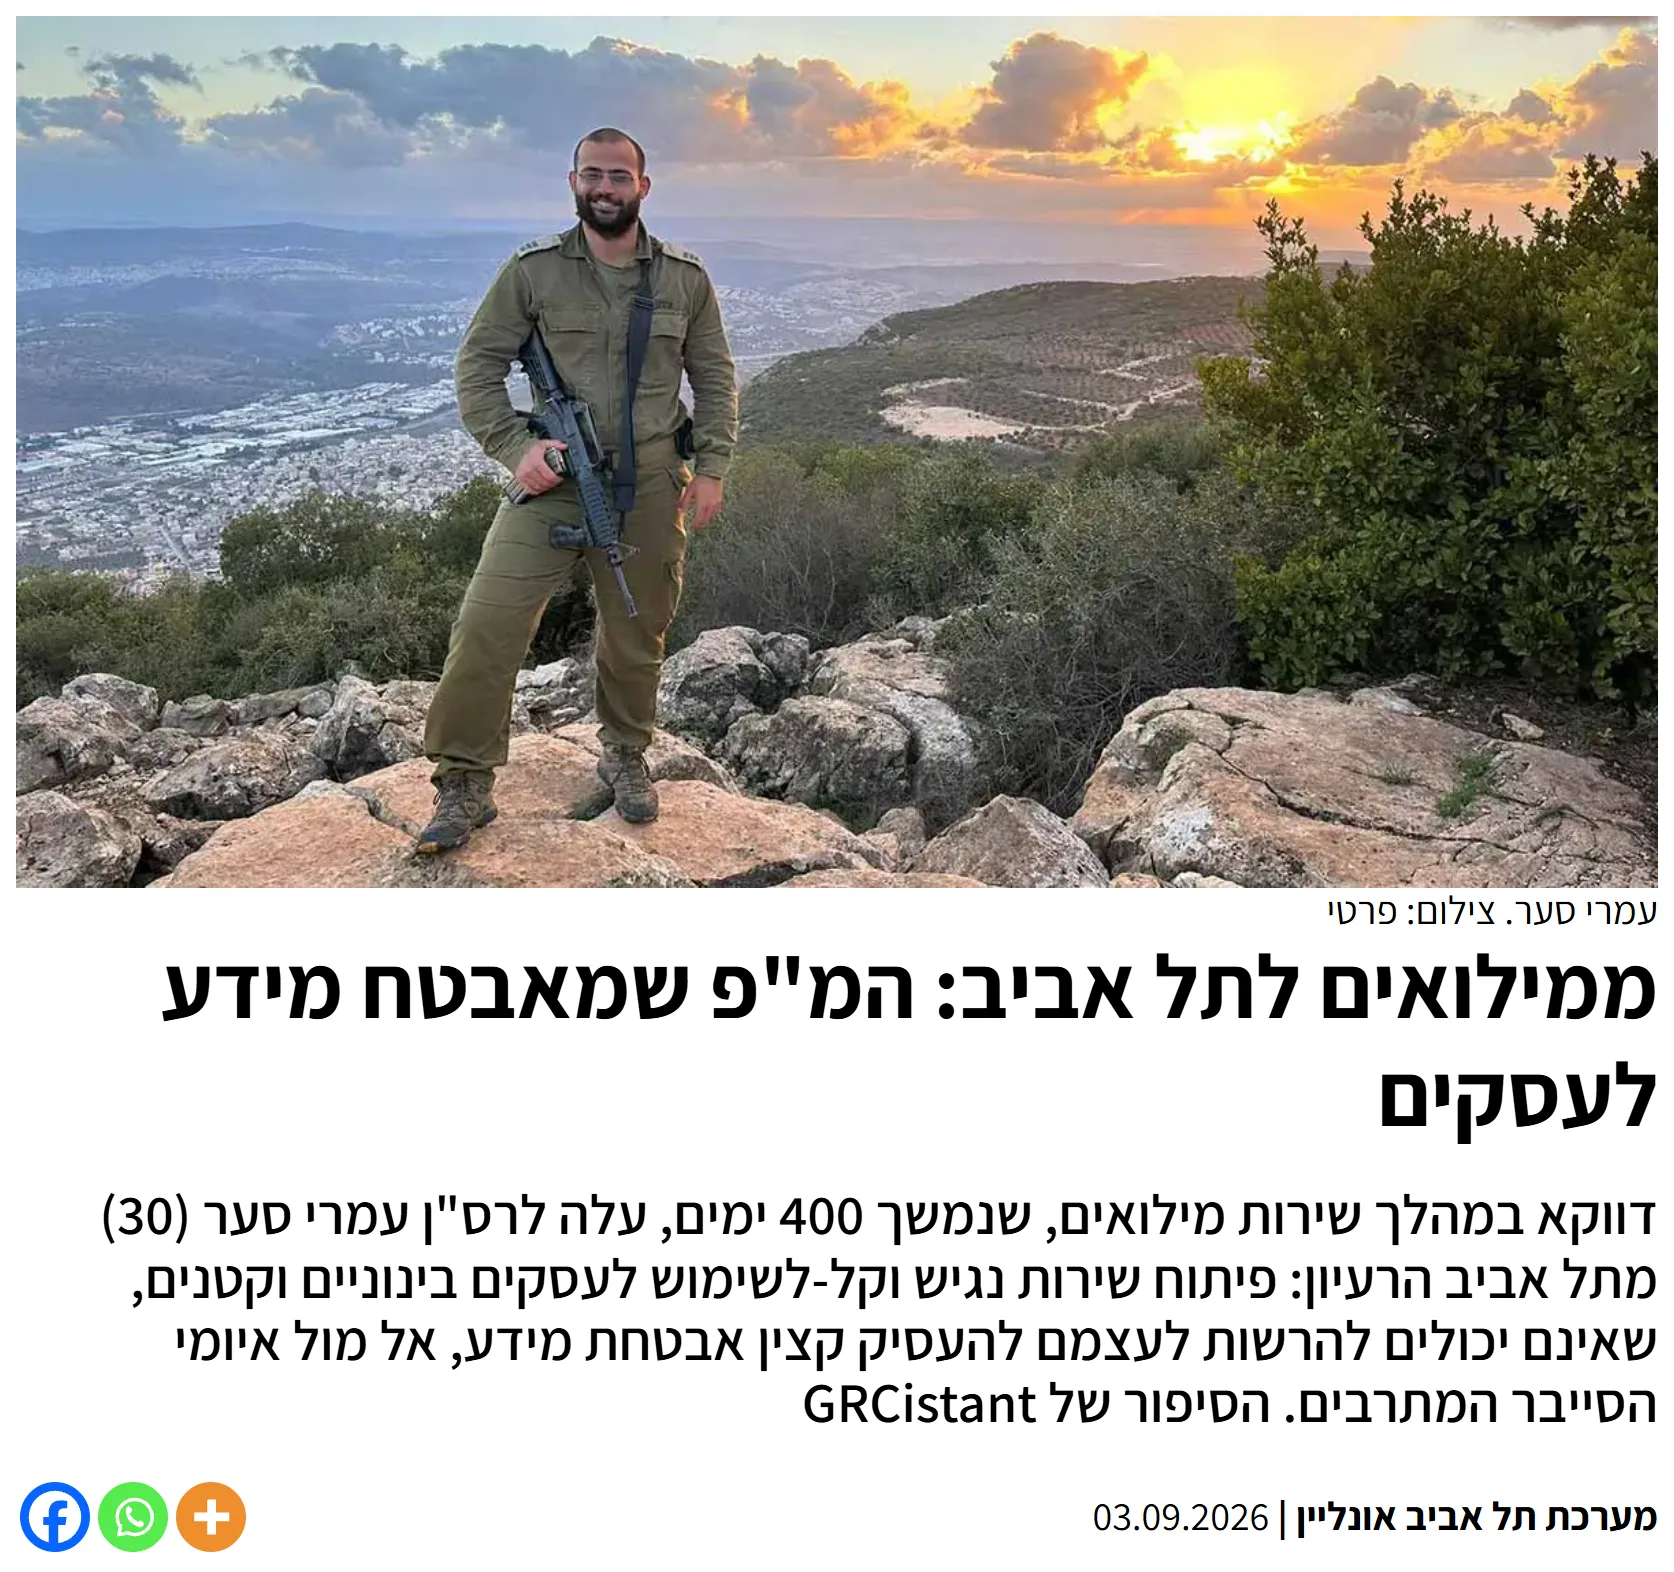
“The system translates the answers through smart logic and produces, in a short time, a risk register, procedures and tailored policy documents.”
Translated from the original
Let's talk
Leave your details and we will come back with a tailored proposal.
- We'll get back to you sooner than you think
- Free first scoping call
- A quote with clear pricing and timeline